 Finland
 Germany
 Denmark
 Sweden
 Italy
 Netherlands
 Norway

Extreme Networks Fabric Connect vs Traditional VLANs: A Strategic Comparison
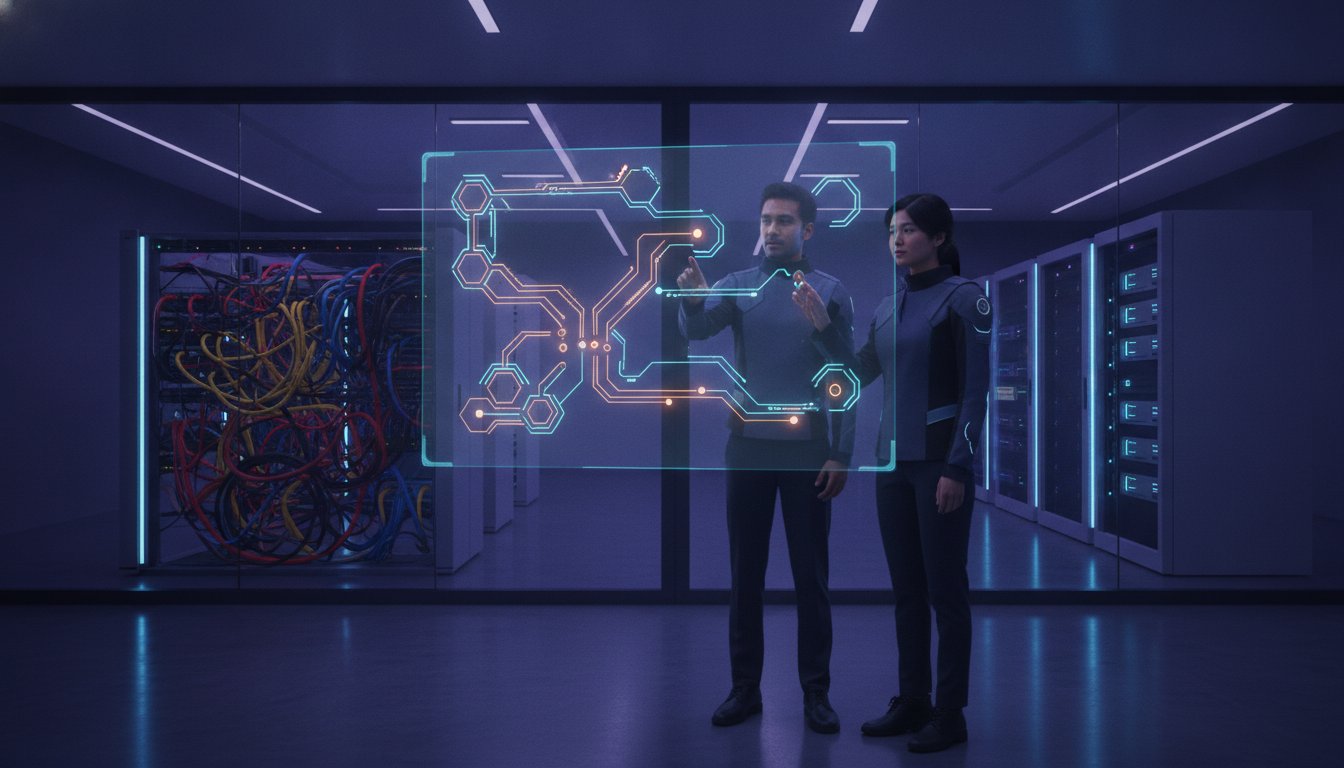
What if your network core never required another manual configuration change, regardless of how many new services you deployed? For many IT leaders, the daily reality of managing enterprise infrastructure still involves the high-risk dance of hop-by-hop VLAN tagging and the constant threat of Spanning Tree Protocol loops. In the strategic comparison of Extreme Networks Fabric Connect vs traditional VLANs, it’s clear that legacy architectures struggle to keep pace with modern demands for agility and security. We understand that your technical team faces significant pressure to reduce service provisioning times across large campuses while maintaining absolute network stability.
This article will demonstrate how transitioning to a Shortest Path Bridging architecture simplifies your operations by automating the core and enabling hyper-segmentation. You’ll gain a comprehensive understanding of how Fabric Connect can reduce manual configuration at the network edge by approximately 90%, providing a clear justification for infrastructure modernization. We’ll examine the technical shift from legacy IEEE 802.1Q standards to the robust IEEE 802.1ah framework to help you achieve faster delivery for every new network service.
The Architecture of Complexity: Limitations of Traditional VLANs
Traditional network architectures rely on the IEEE 802.1Q standard, which necessitates a manual, hop-by-hop approach to configuration. Every switch in the communication path must be individually updated to support a new service. This method creates significant management overhead and introduces numerous opportunities for human error. When evaluating Extreme Networks Fabric Connect vs traditional VLANs, the contrast in operational efficiency becomes immediately apparent. In legacy environments, extending a single VLAN across multiple data centers often leads to “VLAN sprawl,” where the complexity of the database makes troubleshooting nearly impossible. Mastering these transitions often begins with Extreme Networks authorised training to understand the underlying shift in logic.
The Spanning Tree Protocol (STP) Burden
To prevent catastrophic network loops, traditional systems depend on STP. This protocol works by logically blocking redundant physical paths, which effectively wastes up to 50% of your available fiber bandwidth. When a link fails, the “convergence time” required for STP to recalculate and unblock a path can range from several seconds to nearly a minute, causing noticeable downtime for critical applications. This instability is a primary driver for moving toward the IEEE 802.1aq standard, which replaces these legacy limitations with more resilient multipath capabilities.
Manual Service Provisioning Hurdles
Provisioning a new service across a core-aggregation-access hierarchy is a fragile process. A single typo in a trunk configuration or a missing tag on an intermediate switch can isolate entire network segments. These manual tagging and trunking requirements don’t just slow down delivery; they create security vulnerabilities through misconfiguration. By comparing Extreme Networks Fabric Connect vs traditional VLANs, it’s clear that the manual burdens of the latter represent a significant strategic liability for growing enterprises. Relying on manual entries across dozens of switches invites inconsistencies that modern fabric architectures simply eliminate.
Extreme Networks Fabric Connect: A Simplified Approach
Extreme Networks Fabric Connect represents a paradigm shift in network design by utilizing a virtualized network architecture that eliminates the need for core-layer re-configuration. Unlike the fragmented protocol stacks of the past, this solution is built upon the IEEE 802.1aq Shortest Path Bridging (SPB) standard. By consolidating all routing and switching functions into a single, link-state protocol (IS-IS), it streamlines the control plane. This consolidation is technically grounded in IETF RFC 6329, which defines the IS-IS extensions necessary to support such a robust fabric. When comparing Extreme Networks Fabric Connect vs traditional VLANs, the primary advantage is the removal of multiple overlay protocols like OSPF, PIM, and STP.
Shortest Path Bridging (SPB) Explained
The intelligence of the fabric lies in its use of IS-IS to create a naturally loop-free topology. This eliminates the inefficiencies of Spanning Tree Protocol, where redundant links remain idle. Instead, SPB leverages Equal Cost Multi-Pathing (ECMP) to ensure all physical links are active and carrying traffic. This approach maximizes hardware ROI by utilizing the full capacity of your infrastructure. Organizations often find that specialized training is the most effective way to help engineering teams master these advanced link-state behaviors.
The “Edge-Only” Provisioning Model
The “edge-only” model is perhaps the most transformative aspect of this architecture. In a legacy environment, adding a new service requires manual configuration at every “hop” from the access layer to the core. With Fabric Connect, services are provisioned only at the entry and exit points (the edge). The core remains service-agnostic, automatically learning and distributing service information without manual intervention. This dramatically reduces maintenance window requirements, as you no longer need to touch the core switches for routine service expansions. It’s a cleaner, more predictable method of scaling enterprise connectivity.
Operational Comparison: Provisioning, Scalability, and Security
Operational excellence is the hallmark of a modern enterprise network. When analyzing Extreme Networks Fabric Connect vs traditional VLANs, the difference in security posture and administrative efficiency is striking. Fabric Connect facilitates hyper-segmentation, allowing for thousands of isolated segments without the complexity of traditional Virtual Routing and Forwarding (VRF) instances. This capability enables IT teams to scale services rapidly while maintaining granular control over every traffic flow. Verified industry data suggests that this architecture can reduce manual configuration at the network edge by approximately 90%.
Hyper-segmentation vs. Traditional ACLs
Traditional VLAN-based security often relies on porous Access Control Lists (ACLs) that are notoriously difficult to maintain across a large campus. These legacy methods frequently suffer from configuration drift and human error. In contrast, Fabric Connect segments traffic at Layer 2 or Layer 3 with zero leakage between zones. This ensures that sensitive data remains isolated from guest users or compromised devices, providing a robust defense against lateral movement within the network.
Stealth Networking and Attack Surface Reduction
A unique differentiator of this architecture is “Stealth Networking.” Within the fabric, nodes do not require IP addresses for the control plane, making them invisible to external scanning tools. This effectively hides the network core from hackers, significantly reducing the available attack surface. It’s a strategic benefit for securing vulnerable IoT devices and guest networks that might otherwise serve as entry points for threats. We invite you to explore our Extreme Networks authorised training to master these security protocols.
By unifying the control plane, this technology simplifies troubleshooting. It reduces the mean time to repair (MTTR) significantly. Provisioning times drop from days to minutes, directly impacting your organization’s agility. This shift allows your staff to focus on strategic initiatives rather than manual maintenance tasks.
Strategic Implementation: Transitioning to Fabric Networking
Implementing a modern fabric requires a fundamental shift in organizational mindset. You move from the tedious task of managing individual boxes to the strategic orchestration of end-to-end services. This evolution ensures that the technical benefits of Extreme Networks Fabric Connect vs traditional VLANs are fully realized within your specific operational context. We recommend initiating this journey with a pilot phase, typically focused on a high-density data center environment or a specific campus wing, to establish a proven fabric seed before a wider rollout.
As an Extreme Networks Authorized Training Partner, we emphasize that professional enablement is the most critical factor for migration success. Preparing your team for the nuances of link-state protocols ensures that the transition is seamless and well-documented. This proactive approach minimizes the risks often associated with legacy network overhauls.
Bridging the Skills Gap
The move to fabric networking necessitates a transition from legacy STP and VLAN logic toward mastery of SPB and IS-IS behaviors. This evolution requires engineers to understand how the control plane handles service distribution without manual tagging. Enrolling in Extreme Networks Fabric Engine training provides the technical foundation needed to manage these automated environments. It’s a vital step for any team looking to eliminate the fragility of manual configuration errors.
Consultancy and Design Best Practices
Successful deployments often rely on precise architectural design and a clear migration roadmap. Professional consultancy helps in creating a robust initial fabric seed that can scale across global campuses without disruption. Insoft Services supports global enterprises by optimizing these complex infrastructures through expert guidance and localized expertise. We focus on enabling your IT staff to design resilient, future-ready architectures that leverage the full power of hyper-segmentation and stealth networking, ensuring your organization remains agile in an ever-changing professional landscape.
Future-Proofing Your Enterprise Infrastructure
Adopting an automated, service-centric architecture is no longer a luxury but a strategic necessity for global enterprises. By evaluating the benefits of Extreme Networks Fabric Connect vs traditional VLANs, it’s clear that the shift toward Shortest Path Bridging eliminates the inherent risks of manual configuration and unstable Spanning Tree environments. You’ve seen how hyper-segmentation and stealth networking significantly reduce your attack surface while increasing operational agility through edge-only provisioning. As an Authorized Extreme Networks Training Partner with global EMEA-wide delivery, we’re dedicated to providing the expert-led technical consultancy and skills your team needs for a successful migration.
We invite you to master modern network architectures with Official Extreme Networks Training at Insoft Services. It’s an investment in your organization’s long-term resilience and technical excellence. We look forward to supporting your professional growth as you build a more secure, efficient network for the future.
Frequently Asked Questions
Does Extreme Networks Fabric Connect require proprietary hardware?
Extreme Networks Fabric Connect requires hardware specifically designed to support the IEEE 802.1aq standard and the Fabric Engine operating system. While the underlying Shortest Path Bridging protocol is an open standard, the full benefits of the fabric architecture are realized through Extreme’s specialized hardware platforms. It’s important to verify that your switches support MAC-in-MAC encapsulation before beginning a deployment of Extreme Networks Fabric Connect vs traditional VLANs.
Can I run Fabric Connect alongside my existing traditional VLANs?
You can certainly operate Fabric Connect alongside your existing traditional VLANs during a phased migration. The architecture supports Transparent Port UNI and VLAN UNI modes, allowing the fabric to carry legacy 802.1Q tagged traffic without disruption. This capability enables organizations to maintain their current core-aggregation-access hierarchy while gradually introducing fabric services to specific campus wings or data center segments to ensure a stable and predictable transition.
How does Fabric Connect improve network recovery times compared to STP?
Fabric Connect significantly improves recovery times by replacing the slow convergence of Spanning Tree Protocol with the rapid link-state updates of IS-IS. In a traditional environment, STP might take up to 30 or 50 seconds to reroute traffic after a link failure. Fabric Connect typically achieves sub-second convergence, ensuring that critical applications and VoIP sessions remain stable even during physical link interruptions or unexpected hardware failures.
Is Fabric Connect more difficult to troubleshoot than traditional networking?
Troubleshooting is actually simplified because the fabric utilizes a single, unified control plane for all Layer 2 and Layer 3 services. In traditional networking, engineers must often correlate data across multiple protocols like OSPF, PIM, and STP. With Fabric Connect, you only manage IS-IS. This reduction in protocol complexity allows technical teams to identify and resolve connectivity issues much faster, lowering the overall mean time to repair.
What are the specific training requirements for a team to manage Fabric Connect?
Managing this architecture requires a shift from legacy 802.1Q logic to mastering Shortest Path Bridging and IS-IS link-state behaviors. We recommend that teams complete official Extreme Networks Fabric Engine training as a foundational step. This specific curriculum covers the configuration of I-SIDs, the implementation of hyper-segmentation, and the management of edge-only provisioning models to ensure your engineers are fully prepared for modern enterprise infrastructure demands.
What if your network core never required another manual configuration change, regardless of how many new services you deployed? For many IT leaders, the daily reality of managing enterprise infrastructure still involves the high-risk dance of hop-by-hop VLAN tagging and the constant threat of Spanning Tree Protocol loops. In the strategic comparison of Extreme Networks Fabric Connect vs traditional VLANs, it’s clear that legacy architectures struggle to keep pace with modern demands for agility and security. We understand that your technical team faces significant pressure to reduce service provisioning times across large campuses while maintaining absolute network stability.
This article will demonstrate how transitioning to a Shortest Path Bridging architecture simplifies your operations by automating the core and enabling hyper-segmentation. You’ll gain a comprehensive understanding of how Fabric Connect can reduce manual configuration at the network edge by approximately 90%, providing a clear justification for infrastructure modernization. We’ll examine the technical shift from legacy IEEE 802.1Q standards to the robust IEEE 802.1ah framework to help you achieve faster delivery for every new network service.
The Architecture of Complexity: Limitations of Traditional VLANs
Traditional network architectures rely on the IEEE 802.1Q standard, which necessitates a manual, hop-by-hop approach to configuration. Every switch in the communication path must be individually updated to support a new service. This method creates significant management overhead and introduces numerous opportunities for human error. When evaluating Extreme Networks Fabric Connect vs traditional VLANs, the contrast in operational efficiency becomes immediately apparent. In legacy environments, extending a single VLAN across multiple data centers often leads to “VLAN sprawl,” where the complexity of the database makes troubleshooting nearly impossible. Mastering these transitions often begins with Extreme Networks authorised training to understand the underlying shift in logic.
The Spanning Tree Protocol (STP) Burden
To prevent catastrophic network loops, traditional systems depend on STP. This protocol works by logically blocking redundant physical paths, which effectively wastes up to 50% of your available fiber bandwidth. When a link fails, the “convergence time” required for STP to recalculate and unblock a path can range from several seconds to nearly a minute, causing noticeable downtime for critical applications. This instability is a primary driver for moving toward the IEEE 802.1aq standard, which replaces these legacy limitations with more resilient multipath capabilities.
Manual Service Provisioning Hurdles
Provisioning a new service across a core-aggregation-access hierarchy is a fragile process. A single typo in a trunk configuration or a missing tag on an intermediate switch can isolate entire network segments. These manual tagging and trunking requirements don’t just slow down delivery; they create security vulnerabilities through misconfiguration. By comparing Extreme Networks Fabric Connect vs traditional VLANs, it’s clear that the manual burdens of the latter represent a significant strategic liability for growing enterprises. Relying on manual entries across dozens of switches invites inconsistencies that modern fabric architectures simply eliminate.
Extreme Networks Fabric Connect: A Simplified Approach
Extreme Networks Fabric Connect represents a paradigm shift in network design by utilizing a virtualized network architecture that eliminates the need for core-layer re-configuration. Unlike the fragmented protocol stacks of the past, this solution is built upon the IEEE 802.1aq Shortest Path Bridging (SPB) standard. By consolidating all routing and switching functions into a single, link-state protocol (IS-IS), it streamlines the control plane. This consolidation is technically grounded in IETF RFC 6329, which defines the IS-IS extensions necessary to support such a robust fabric. When comparing Extreme Networks Fabric Connect vs traditional VLANs, the primary advantage is the removal of multiple overlay protocols like OSPF, PIM, and STP.
Shortest Path Bridging (SPB) Explained
The intelligence of the fabric lies in its use of IS-IS to create a naturally loop-free topology. This eliminates the inefficiencies of Spanning Tree Protocol, where redundant links remain idle. Instead, SPB leverages Equal Cost Multi-Pathing (ECMP) to ensure all physical links are active and carrying traffic. This approach maximizes hardware ROI by utilizing the full capacity of your infrastructure. Organizations often find that specialized training is the most effective way to help engineering teams master these advanced link-state behaviors.
The “Edge-Only” Provisioning Model
The “edge-only” model is perhaps the most transformative aspect of this architecture. In a legacy environment, adding a new service requires manual configuration at every “hop” from the access layer to the core. With Fabric Connect, services are provisioned only at the entry and exit points (the edge). The core remains service-agnostic, automatically learning and distributing service information without manual intervention. This dramatically reduces maintenance window requirements, as you no longer need to touch the core switches for routine service expansions. It’s a cleaner, more predictable method of scaling enterprise connectivity.
Operational Comparison: Provisioning, Scalability, and Security
Operational excellence is the hallmark of a modern enterprise network. When analyzing Extreme Networks Fabric Connect vs traditional VLANs, the difference in security posture and administrative efficiency is striking. Fabric Connect facilitates hyper-segmentation, allowing for thousands of isolated segments without the complexity of traditional Virtual Routing and Forwarding (VRF) instances. This capability enables IT teams to scale services rapidly while maintaining granular control over every traffic flow. Verified industry data suggests that this architecture can reduce manual configuration at the network edge by approximately 90%.
Hyper-segmentation vs. Traditional ACLs
Traditional VLAN-based security often relies on porous Access Control Lists (ACLs) that are notoriously difficult to maintain across a large campus. These legacy methods frequently suffer from configuration drift and human error. In contrast, Fabric Connect segments traffic at Layer 2 or Layer 3 with zero leakage between zones. This ensures that sensitive data remains isolated from guest users or compromised devices, providing a robust defense against lateral movement within the network.
Stealth Networking and Attack Surface Reduction
A unique differentiator of this architecture is “Stealth Networking.” Within the fabric, nodes do not require IP addresses for the control plane, making them invisible to external scanning tools. This effectively hides the network core from hackers, significantly reducing the available attack surface. It’s a strategic benefit for securing vulnerable IoT devices and guest networks that might otherwise serve as entry points for threats. We invite you to explore our Extreme Networks authorised training to master these security protocols.
By unifying the control plane, this technology simplifies troubleshooting. It reduces the mean time to repair (MTTR) significantly. Provisioning times drop from days to minutes, directly impacting your organization’s agility. This shift allows your staff to focus on strategic initiatives rather than manual maintenance tasks.
Strategic Implementation: Transitioning to Fabric Networking
Implementing a modern fabric requires a fundamental shift in organizational mindset. You move from the tedious task of managing individual boxes to the strategic orchestration of end-to-end services. This evolution ensures that the technical benefits of Extreme Networks Fabric Connect vs traditional VLANs are fully realized within your specific operational context. We recommend initiating this journey with a pilot phase, typically focused on a high-density data center environment or a specific campus wing, to establish a proven fabric seed before a wider rollout.
As an Extreme Networks Authorized Training Partner, we emphasize that professional enablement is the most critical factor for migration success. Preparing your team for the nuances of link-state protocols ensures that the transition is seamless and well-documented. This proactive approach minimizes the risks often associated with legacy network overhauls.
Bridging the Skills Gap
The move to fabric networking necessitates a transition from legacy STP and VLAN logic toward mastery of SPB and IS-IS behaviors. This evolution requires engineers to understand how the control plane handles service distribution without manual tagging. Enrolling in Extreme Networks Fabric Engine training provides the technical foundation needed to manage these automated environments. It’s a vital step for any team looking to eliminate the fragility of manual configuration errors.
Consultancy and Design Best Practices
Successful deployments often rely on precise architectural design and a clear migration roadmap. Professional consultancy helps in creating a robust initial fabric seed that can scale across global campuses without disruption. Insoft Services supports global enterprises by optimizing these complex infrastructures through expert guidance and localized expertise. We focus on enabling your IT staff to design resilient, future-ready architectures that leverage the full power of hyper-segmentation and stealth networking, ensuring your organization remains agile in an ever-changing professional landscape.
Future-Proofing Your Enterprise Infrastructure
Adopting an automated, service-centric architecture is no longer a luxury but a strategic necessity for global enterprises. By evaluating the benefits of Extreme Networks Fabric Connect vs traditional VLANs, it’s clear that the shift toward Shortest Path Bridging eliminates the inherent risks of manual configuration and unstable Spanning Tree environments. You’ve seen how hyper-segmentation and stealth networking significantly reduce your attack surface while increasing operational agility through edge-only provisioning. As an Authorized Extreme Networks Training Partner with global EMEA-wide delivery, we’re dedicated to providing the expert-led technical consultancy and skills your team needs for a successful migration.
We invite you to master modern network architectures with Official Extreme Networks Training at Insoft Services. It’s an investment in your organization’s long-term resilience and technical excellence. We look forward to supporting your professional growth as you build a more secure, efficient network for the future.
Frequently Asked Questions
Does Extreme Networks Fabric Connect require proprietary hardware?
Extreme Networks Fabric Connect requires hardware specifically designed to support the IEEE 802.1aq standard and the Fabric Engine operating system. While the underlying Shortest Path Bridging protocol is an open standard, the full benefits of the fabric architecture are realized through Extreme’s specialized hardware platforms. It’s important to verify that your switches support MAC-in-MAC encapsulation before beginning a deployment of Extreme Networks Fabric Connect vs traditional VLANs.
Can I run Fabric Connect alongside my existing traditional VLANs?
You can certainly operate Fabric Connect alongside your existing traditional VLANs during a phased migration. The architecture supports Transparent Port UNI and VLAN UNI modes, allowing the fabric to carry legacy 802.1Q tagged traffic without disruption. This capability enables organizations to maintain their current core-aggregation-access hierarchy while gradually introducing fabric services to specific campus wings or data center segments to ensure a stable and predictable transition.
How does Fabric Connect improve network recovery times compared to STP?
Fabric Connect significantly improves recovery times by replacing the slow convergence of Spanning Tree Protocol with the rapid link-state updates of IS-IS. In a traditional environment, STP might take up to 30 or 50 seconds to reroute traffic after a link failure. Fabric Connect typically achieves sub-second convergence, ensuring that critical applications and VoIP sessions remain stable even during physical link interruptions or unexpected hardware failures.
Is Fabric Connect more difficult to troubleshoot than traditional networking?
Troubleshooting is actually simplified because the fabric utilizes a single, unified control plane for all Layer 2 and Layer 3 services. In traditional networking, engineers must often correlate data across multiple protocols like OSPF, PIM, and STP. With Fabric Connect, you only manage IS-IS. This reduction in protocol complexity allows technical teams to identify and resolve connectivity issues much faster, lowering the overall mean time to repair.
What are the specific training requirements for a team to manage Fabric Connect?
Managing this architecture requires a shift from legacy 802.1Q logic to mastering Shortest Path Bridging and IS-IS link-state behaviors. We recommend that teams complete official Extreme Networks Fabric Engine training as a foundational step. This specific curriculum covers the configuration of I-SIDs, the implementation of hyper-segmentation, and the management of edge-only provisioning models to ensure your engineers are fully prepared for modern enterprise infrastructure demands.
What if your network core never required another manual configuration change, regardless of how many new services you deployed? For many IT leaders, the daily reality of managing enterprise infrastructure still involves the high-risk dance of hop-by-hop VLAN tagging and the constant threat of Spanning Tree Protocol loops. In the strategic comparison of Extreme Networks Fabric Connect vs traditional VLANs, it’s clear that legacy architectures struggle to keep pace with modern demands for agility and security. We understand that your technical team faces significant pressure to reduce service provisioning times across large campuses while maintaining absolute network stability.
This article will demonstrate how transitioning to a Shortest Path Bridging architecture simplifies your operations by automating the core and enabling hyper-segmentation. You’ll gain a comprehensive understanding of how Fabric Connect can reduce manual configuration at the network edge by approximately 90%, providing a clear justification for infrastructure modernization. We’ll examine the technical shift from legacy IEEE 802.1Q standards to the robust IEEE 802.1ah framework to help you achieve faster delivery for every new network service.
The Architecture of Complexity: Limitations of Traditional VLANs
Traditional network architectures rely on the IEEE 802.1Q standard, which necessitates a manual, hop-by-hop approach to configuration. Every switch in the communication path must be individually updated to support a new service. This method creates significant management overhead and introduces numerous opportunities for human error. When evaluating Extreme Networks Fabric Connect vs traditional VLANs, the contrast in operational efficiency becomes immediately apparent. In legacy environments, extending a single VLAN across multiple data centers often leads to “VLAN sprawl,” where the complexity of the database makes troubleshooting nearly impossible. Mastering these transitions often begins with Extreme Networks authorised training to understand the underlying shift in logic.
The Spanning Tree Protocol (STP) Burden
To prevent catastrophic network loops, traditional systems depend on STP. This protocol works by logically blocking redundant physical paths, which effectively wastes up to 50% of your available fiber bandwidth. When a link fails, the “convergence time” required for STP to recalculate and unblock a path can range from several seconds to nearly a minute, causing noticeable downtime for critical applications. This instability is a primary driver for moving toward the IEEE 802.1aq standard, which replaces these legacy limitations with more resilient multipath capabilities.
Manual Service Provisioning Hurdles
Provisioning a new service across a core-aggregation-access hierarchy is a fragile process. A single typo in a trunk configuration or a missing tag on an intermediate switch can isolate entire network segments. These manual tagging and trunking requirements don’t just slow down delivery; they create security vulnerabilities through misconfiguration. By comparing Extreme Networks Fabric Connect vs traditional VLANs, it’s clear that the manual burdens of the latter represent a significant strategic liability for growing enterprises. Relying on manual entries across dozens of switches invites inconsistencies that modern fabric architectures simply eliminate.
Extreme Networks Fabric Connect: A Simplified Approach
Extreme Networks Fabric Connect represents a paradigm shift in network design by utilizing a virtualized network architecture that eliminates the need for core-layer re-configuration. Unlike the fragmented protocol stacks of the past, this solution is built upon the IEEE 802.1aq Shortest Path Bridging (SPB) standard. By consolidating all routing and switching functions into a single, link-state protocol (IS-IS), it streamlines the control plane. This consolidation is technically grounded in IETF RFC 6329, which defines the IS-IS extensions necessary to support such a robust fabric. When comparing Extreme Networks Fabric Connect vs traditional VLANs, the primary advantage is the removal of multiple overlay protocols like OSPF, PIM, and STP.
Shortest Path Bridging (SPB) Explained
The intelligence of the fabric lies in its use of IS-IS to create a naturally loop-free topology. This eliminates the inefficiencies of Spanning Tree Protocol, where redundant links remain idle. Instead, SPB leverages Equal Cost Multi-Pathing (ECMP) to ensure all physical links are active and carrying traffic. This approach maximizes hardware ROI by utilizing the full capacity of your infrastructure. Organizations often find that specialized training is the most effective way to help engineering teams master these advanced link-state behaviors.
The “Edge-Only” Provisioning Model
The “edge-only” model is perhaps the most transformative aspect of this architecture. In a legacy environment, adding a new service requires manual configuration at every “hop” from the access layer to the core. With Fabric Connect, services are provisioned only at the entry and exit points (the edge). The core remains service-agnostic, automatically learning and distributing service information without manual intervention. This dramatically reduces maintenance window requirements, as you no longer need to touch the core switches for routine service expansions. It’s a cleaner, more predictable method of scaling enterprise connectivity.
Operational Comparison: Provisioning, Scalability, and Security
Operational excellence is the hallmark of a modern enterprise network. When analyzing Extreme Networks Fabric Connect vs traditional VLANs, the difference in security posture and administrative efficiency is striking. Fabric Connect facilitates hyper-segmentation, allowing for thousands of isolated segments without the complexity of traditional Virtual Routing and Forwarding (VRF) instances. This capability enables IT teams to scale services rapidly while maintaining granular control over every traffic flow. Verified industry data suggests that this architecture can reduce manual configuration at the network edge by approximately 90%.
Hyper-segmentation vs. Traditional ACLs
Traditional VLAN-based security often relies on porous Access Control Lists (ACLs) that are notoriously difficult to maintain across a large campus. These legacy methods frequently suffer from configuration drift and human error. In contrast, Fabric Connect segments traffic at Layer 2 or Layer 3 with zero leakage between zones. This ensures that sensitive data remains isolated from guest users or compromised devices, providing a robust defense against lateral movement within the network.
Stealth Networking and Attack Surface Reduction
A unique differentiator of this architecture is “Stealth Networking.” Within the fabric, nodes do not require IP addresses for the control plane, making them invisible to external scanning tools. This effectively hides the network core from hackers, significantly reducing the available attack surface. It’s a strategic benefit for securing vulnerable IoT devices and guest networks that might otherwise serve as entry points for threats. We invite you to explore our Extreme Networks authorised training to master these security protocols.
By unifying the control plane, this technology simplifies troubleshooting. It reduces the mean time to repair (MTTR) significantly. Provisioning times drop from days to minutes, directly impacting your organization’s agility. This shift allows your staff to focus on strategic initiatives rather than manual maintenance tasks.
Strategic Implementation: Transitioning to Fabric Networking
Implementing a modern fabric requires a fundamental shift in organizational mindset. You move from the tedious task of managing individual boxes to the strategic orchestration of end-to-end services. This evolution ensures that the technical benefits of Extreme Networks Fabric Connect vs traditional VLANs are fully realized within your specific operational context. We recommend initiating this journey with a pilot phase, typically focused on a high-density data center environment or a specific campus wing, to establish a proven fabric seed before a wider rollout.
As an Extreme Networks Authorized Training Partner, we emphasize that professional enablement is the most critical factor for migration success. Preparing your team for the nuances of link-state protocols ensures that the transition is seamless and well-documented. This proactive approach minimizes the risks often associated with legacy network overhauls.
Bridging the Skills Gap
The move to fabric networking necessitates a transition from legacy STP and VLAN logic toward mastery of SPB and IS-IS behaviors. This evolution requires engineers to understand how the control plane handles service distribution without manual tagging. Enrolling in Extreme Networks Fabric Engine training provides the technical foundation needed to manage these automated environments. It’s a vital step for any team looking to eliminate the fragility of manual configuration errors.
Consultancy and Design Best Practices
Successful deployments often rely on precise architectural design and a clear migration roadmap. Professional consultancy helps in creating a robust initial fabric seed that can scale across global campuses without disruption. Insoft Services supports global enterprises by optimizing these complex infrastructures through expert guidance and localized expertise. We focus on enabling your IT staff to design resilient, future-ready architectures that leverage the full power of hyper-segmentation and stealth networking, ensuring your organization remains agile in an ever-changing professional landscape.
Future-Proofing Your Enterprise Infrastructure
Adopting an automated, service-centric architecture is no longer a luxury but a strategic necessity for global enterprises. By evaluating the benefits of Extreme Networks Fabric Connect vs traditional VLANs, it’s clear that the shift toward Shortest Path Bridging eliminates the inherent risks of manual configuration and unstable Spanning Tree environments. You’ve seen how hyper-segmentation and stealth networking significantly reduce your attack surface while increasing operational agility through edge-only provisioning. As an Authorized Extreme Networks Training Partner with global EMEA-wide delivery, we’re dedicated to providing the expert-led technical consultancy and skills your team needs for a successful migration.
We invite you to master modern network architectures with Official Extreme Networks Training at Insoft Services. It’s an investment in your organization’s long-term resilience and technical excellence. We look forward to supporting your professional growth as you build a more secure, efficient network for the future.
Frequently Asked Questions
Does Extreme Networks Fabric Connect require proprietary hardware?
Extreme Networks Fabric Connect requires hardware specifically designed to support the IEEE 802.1aq standard and the Fabric Engine operating system. While the underlying Shortest Path Bridging protocol is an open standard, the full benefits of the fabric architecture are realized through Extreme’s specialized hardware platforms. It’s important to verify that your switches support MAC-in-MAC encapsulation before beginning a deployment of Extreme Networks Fabric Connect vs traditional VLANs.
Can I run Fabric Connect alongside my existing traditional VLANs?
You can certainly operate Fabric Connect alongside your existing traditional VLANs during a phased migration. The architecture supports Transparent Port UNI and VLAN UNI modes, allowing the fabric to carry legacy 802.1Q tagged traffic without disruption. This capability enables organizations to maintain their current core-aggregation-access hierarchy while gradually introducing fabric services to specific campus wings or data center segments to ensure a stable and predictable transition.
How does Fabric Connect improve network recovery times compared to STP?
Fabric Connect significantly improves recovery times by replacing the slow convergence of Spanning Tree Protocol with the rapid link-state updates of IS-IS. In a traditional environment, STP might take up to 30 or 50 seconds to reroute traffic after a link failure. Fabric Connect typically achieves sub-second convergence, ensuring that critical applications and VoIP sessions remain stable even during physical link interruptions or unexpected hardware failures.
Is Fabric Connect more difficult to troubleshoot than traditional networking?
Troubleshooting is actually simplified because the fabric utilizes a single, unified control plane for all Layer 2 and Layer 3 services. In traditional networking, engineers must often correlate data across multiple protocols like OSPF, PIM, and STP. With Fabric Connect, you only manage IS-IS. This reduction in protocol complexity allows technical teams to identify and resolve connectivity issues much faster, lowering the overall mean time to repair.
What are the specific training requirements for a team to manage Fabric Connect?
Managing this architecture requires a shift from legacy 802.1Q logic to mastering Shortest Path Bridging and IS-IS link-state behaviors. We recommend that teams complete official Extreme Networks Fabric Engine training as a foundational step. This specific curriculum covers the configuration of I-SIDs, the implementation of hyper-segmentation, and the management of edge-only provisioning models to ensure your engineers are fully prepared for modern enterprise infrastructure demands.
What if your network core never required another manual configuration change, regardless of how many new services you deployed? For many IT leaders, the daily reality of managing enterprise infrastructure still involves the high-risk dance of hop-by-hop VLAN tagging and the constant threat of Spanning Tree Protocol loops. In the strategic comparison of Extreme Networks Fabric Connect vs traditional VLANs, it’s clear that legacy architectures struggle to keep pace with modern demands for agility and security. We understand that your technical team faces significant pressure to reduce service provisioning times across large campuses while maintaining absolute network stability.
This article will demonstrate how transitioning to a Shortest Path Bridging architecture simplifies your operations by automating the core and enabling hyper-segmentation. You’ll gain a comprehensive understanding of how Fabric Connect can reduce manual configuration at the network edge by approximately 90%, providing a clear justification for infrastructure modernization. We’ll examine the technical shift from legacy IEEE 802.1Q standards to the robust IEEE 802.1ah framework to help you achieve faster delivery for every new network service.
The Architecture of Complexity: Limitations of Traditional VLANs
Traditional network architectures rely on the IEEE 802.1Q standard, which necessitates a manual, hop-by-hop approach to configuration. Every switch in the communication path must be individually updated to support a new service. This method creates significant management overhead and introduces numerous opportunities for human error. When evaluating Extreme Networks Fabric Connect vs traditional VLANs, the contrast in operational efficiency becomes immediately apparent. In legacy environments, extending a single VLAN across multiple data centers often leads to “VLAN sprawl,” where the complexity of the database makes troubleshooting nearly impossible. Mastering these transitions often begins with Extreme Networks authorised training to understand the underlying shift in logic.
The Spanning Tree Protocol (STP) Burden
To prevent catastrophic network loops, traditional systems depend on STP. This protocol works by logically blocking redundant physical paths, which effectively wastes up to 50% of your available fiber bandwidth. When a link fails, the “convergence time” required for STP to recalculate and unblock a path can range from several seconds to nearly a minute, causing noticeable downtime for critical applications. This instability is a primary driver for moving toward the IEEE 802.1aq standard, which replaces these legacy limitations with more resilient multipath capabilities.
Manual Service Provisioning Hurdles
Provisioning a new service across a core-aggregation-access hierarchy is a fragile process. A single typo in a trunk configuration or a missing tag on an intermediate switch can isolate entire network segments. These manual tagging and trunking requirements don’t just slow down delivery; they create security vulnerabilities through misconfiguration. By comparing Extreme Networks Fabric Connect vs traditional VLANs, it’s clear that the manual burdens of the latter represent a significant strategic liability for growing enterprises. Relying on manual entries across dozens of switches invites inconsistencies that modern fabric architectures simply eliminate.
Extreme Networks Fabric Connect: A Simplified Approach
Extreme Networks Fabric Connect represents a paradigm shift in network design by utilizing a virtualized network architecture that eliminates the need for core-layer re-configuration. Unlike the fragmented protocol stacks of the past, this solution is built upon the IEEE 802.1aq Shortest Path Bridging (SPB) standard. By consolidating all routing and switching functions into a single, link-state protocol (IS-IS), it streamlines the control plane. This consolidation is technically grounded in IETF RFC 6329, which defines the IS-IS extensions necessary to support such a robust fabric. When comparing Extreme Networks Fabric Connect vs traditional VLANs, the primary advantage is the removal of multiple overlay protocols like OSPF, PIM, and STP.
Shortest Path Bridging (SPB) Explained
The intelligence of the fabric lies in its use of IS-IS to create a naturally loop-free topology. This eliminates the inefficiencies of Spanning Tree Protocol, where redundant links remain idle. Instead, SPB leverages Equal Cost Multi-Pathing (ECMP) to ensure all physical links are active and carrying traffic. This approach maximizes hardware ROI by utilizing the full capacity of your infrastructure. Organizations often find that specialized training is the most effective way to help engineering teams master these advanced link-state behaviors.
The “Edge-Only” Provisioning Model
The “edge-only” model is perhaps the most transformative aspect of this architecture. In a legacy environment, adding a new service requires manual configuration at every “hop” from the access layer to the core. With Fabric Connect, services are provisioned only at the entry and exit points (the edge). The core remains service-agnostic, automatically learning and distributing service information without manual intervention. This dramatically reduces maintenance window requirements, as you no longer need to touch the core switches for routine service expansions. It’s a cleaner, more predictable method of scaling enterprise connectivity.
Operational Comparison: Provisioning, Scalability, and Security
Operational excellence is the hallmark of a modern enterprise network. When analyzing Extreme Networks Fabric Connect vs traditional VLANs, the difference in security posture and administrative efficiency is striking. Fabric Connect facilitates hyper-segmentation, allowing for thousands of isolated segments without the complexity of traditional Virtual Routing and Forwarding (VRF) instances. This capability enables IT teams to scale services rapidly while maintaining granular control over every traffic flow. Verified industry data suggests that this architecture can reduce manual configuration at the network edge by approximately 90%.
Hyper-segmentation vs. Traditional ACLs
Traditional VLAN-based security often relies on porous Access Control Lists (ACLs) that are notoriously difficult to maintain across a large campus. These legacy methods frequently suffer from configuration drift and human error. In contrast, Fabric Connect segments traffic at Layer 2 or Layer 3 with zero leakage between zones. This ensures that sensitive data remains isolated from guest users or compromised devices, providing a robust defense against lateral movement within the network.
Stealth Networking and Attack Surface Reduction
A unique differentiator of this architecture is “Stealth Networking.” Within the fabric, nodes do not require IP addresses for the control plane, making them invisible to external scanning tools. This effectively hides the network core from hackers, significantly reducing the available attack surface. It’s a strategic benefit for securing vulnerable IoT devices and guest networks that might otherwise serve as entry points for threats. We invite you to explore our Extreme Networks authorised training to master these security protocols.
By unifying the control plane, this technology simplifies troubleshooting. It reduces the mean time to repair (MTTR) significantly. Provisioning times drop from days to minutes, directly impacting your organization’s agility. This shift allows your staff to focus on strategic initiatives rather than manual maintenance tasks.
Strategic Implementation: Transitioning to Fabric Networking
Implementing a modern fabric requires a fundamental shift in organizational mindset. You move from the tedious task of managing individual boxes to the strategic orchestration of end-to-end services. This evolution ensures that the technical benefits of Extreme Networks Fabric Connect vs traditional VLANs are fully realized within your specific operational context. We recommend initiating this journey with a pilot phase, typically focused on a high-density data center environment or a specific campus wing, to establish a proven fabric seed before a wider rollout.
As an Extreme Networks Authorized Training Partner, we emphasize that professional enablement is the most critical factor for migration success. Preparing your team for the nuances of link-state protocols ensures that the transition is seamless and well-documented. This proactive approach minimizes the risks often associated with legacy network overhauls.
Bridging the Skills Gap
The move to fabric networking necessitates a transition from legacy STP and VLAN logic toward mastery of SPB and IS-IS behaviors. This evolution requires engineers to understand how the control plane handles service distribution without manual tagging. Enrolling in Extreme Networks Fabric Engine training provides the technical foundation needed to manage these automated environments. It’s a vital step for any team looking to eliminate the fragility of manual configuration errors.
Consultancy and Design Best Practices
Successful deployments often rely on precise architectural design and a clear migration roadmap. Professional consultancy helps in creating a robust initial fabric seed that can scale across global campuses without disruption. Insoft Services supports global enterprises by optimizing these complex infrastructures through expert guidance and localized expertise. We focus on enabling your IT staff to design resilient, future-ready architectures that leverage the full power of hyper-segmentation and stealth networking, ensuring your organization remains agile in an ever-changing professional landscape.
Future-Proofing Your Enterprise Infrastructure
Adopting an automated, service-centric architecture is no longer a luxury but a strategic necessity for global enterprises. By evaluating the benefits of Extreme Networks Fabric Connect vs traditional VLANs, it’s clear that the shift toward Shortest Path Bridging eliminates the inherent risks of manual configuration and unstable Spanning Tree environments. You’ve seen how hyper-segmentation and stealth networking significantly reduce your attack surface while increasing operational agility through edge-only provisioning. As an Authorized Extreme Networks Training Partner with global EMEA-wide delivery, we’re dedicated to providing the expert-led technical consultancy and skills your team needs for a successful migration.
We invite you to master modern network architectures with Official Extreme Networks Training at Insoft Services. It’s an investment in your organization’s long-term resilience and technical excellence. We look forward to supporting your professional growth as you build a more secure, efficient network for the future.
Frequently Asked Questions
Does Extreme Networks Fabric Connect require proprietary hardware?
Extreme Networks Fabric Connect requires hardware specifically designed to support the IEEE 802.1aq standard and the Fabric Engine operating system. While the underlying Shortest Path Bridging protocol is an open standard, the full benefits of the fabric architecture are realized through Extreme’s specialized hardware platforms. It’s important to verify that your switches support MAC-in-MAC encapsulation before beginning a deployment of Extreme Networks Fabric Connect vs traditional VLANs.
Can I run Fabric Connect alongside my existing traditional VLANs?
You can certainly operate Fabric Connect alongside your existing traditional VLANs during a phased migration. The architecture supports Transparent Port UNI and VLAN UNI modes, allowing the fabric to carry legacy 802.1Q tagged traffic without disruption. This capability enables organizations to maintain their current core-aggregation-access hierarchy while gradually introducing fabric services to specific campus wings or data center segments to ensure a stable and predictable transition.
How does Fabric Connect improve network recovery times compared to STP?
Fabric Connect significantly improves recovery times by replacing the slow convergence of Spanning Tree Protocol with the rapid link-state updates of IS-IS. In a traditional environment, STP might take up to 30 or 50 seconds to reroute traffic after a link failure. Fabric Connect typically achieves sub-second convergence, ensuring that critical applications and VoIP sessions remain stable even during physical link interruptions or unexpected hardware failures.
Is Fabric Connect more difficult to troubleshoot than traditional networking?
Troubleshooting is actually simplified because the fabric utilizes a single, unified control plane for all Layer 2 and Layer 3 services. In traditional networking, engineers must often correlate data across multiple protocols like OSPF, PIM, and STP. With Fabric Connect, you only manage IS-IS. This reduction in protocol complexity allows technical teams to identify and resolve connectivity issues much faster, lowering the overall mean time to repair.
What are the specific training requirements for a team to manage Fabric Connect?
Managing this architecture requires a shift from legacy 802.1Q logic to mastering Shortest Path Bridging and IS-IS link-state behaviors. We recommend that teams complete official Extreme Networks Fabric Engine training as a foundational step. This specific curriculum covers the configuration of I-SIDs, the implementation of hyper-segmentation, and the management of edge-only provisioning models to ensure your engineers are fully prepared for modern enterprise infrastructure demands.
What if your network core never required another manual configuration change, regardless of how many new services you deployed? For many IT leaders, the daily reality of managing enterprise infrastructure still involves the high-risk dance of hop-by-hop VLAN tagging and the constant threat of Spanning Tree Protocol loops. In the strategic comparison of Extreme Networks Fabric Connect vs traditional VLANs, it’s clear that legacy architectures struggle to keep pace with modern demands for agility and security. We understand that your technical team faces significant pressure to reduce service provisioning times across large campuses while maintaining absolute network stability.
This article will demonstrate how transitioning to a Shortest Path Bridging architecture simplifies your operations by automating the core and enabling hyper-segmentation. You’ll gain a comprehensive understanding of how Fabric Connect can reduce manual configuration at the network edge by approximately 90%, providing a clear justification for infrastructure modernization. We’ll examine the technical shift from legacy IEEE 802.1Q standards to the robust IEEE 802.1ah framework to help you achieve faster delivery for every new network service.
The Architecture of Complexity: Limitations of Traditional VLANs
Traditional network architectures rely on the IEEE 802.1Q standard, which necessitates a manual, hop-by-hop approach to configuration. Every switch in the communication path must be individually updated to support a new service. This method creates significant management overhead and introduces numerous opportunities for human error. When evaluating Extreme Networks Fabric Connect vs traditional VLANs, the contrast in operational efficiency becomes immediately apparent. In legacy environments, extending a single VLAN across multiple data centers often leads to “VLAN sprawl,” where the complexity of the database makes troubleshooting nearly impossible. Mastering these transitions often begins with Extreme Networks authorised training to understand the underlying shift in logic.
The Spanning Tree Protocol (STP) Burden
To prevent catastrophic network loops, traditional systems depend on STP. This protocol works by logically blocking redundant physical paths, which effectively wastes up to 50% of your available fiber bandwidth. When a link fails, the “convergence time” required for STP to recalculate and unblock a path can range from several seconds to nearly a minute, causing noticeable downtime for critical applications. This instability is a primary driver for moving toward the IEEE 802.1aq standard, which replaces these legacy limitations with more resilient multipath capabilities.
Manual Service Provisioning Hurdles
Provisioning a new service across a core-aggregation-access hierarchy is a fragile process. A single typo in a trunk configuration or a missing tag on an intermediate switch can isolate entire network segments. These manual tagging and trunking requirements don’t just slow down delivery; they create security vulnerabilities through misconfiguration. By comparing Extreme Networks Fabric Connect vs traditional VLANs, it’s clear that the manual burdens of the latter represent a significant strategic liability for growing enterprises. Relying on manual entries across dozens of switches invites inconsistencies that modern fabric architectures simply eliminate.
Extreme Networks Fabric Connect: A Simplified Approach
Extreme Networks Fabric Connect represents a paradigm shift in network design by utilizing a virtualized network architecture that eliminates the need for core-layer re-configuration. Unlike the fragmented protocol stacks of the past, this solution is built upon the IEEE 802.1aq Shortest Path Bridging (SPB) standard. By consolidating all routing and switching functions into a single, link-state protocol (IS-IS), it streamlines the control plane. This consolidation is technically grounded in IETF RFC 6329, which defines the IS-IS extensions necessary to support such a robust fabric. When comparing Extreme Networks Fabric Connect vs traditional VLANs, the primary advantage is the removal of multiple overlay protocols like OSPF, PIM, and STP.
Shortest Path Bridging (SPB) Explained
The intelligence of the fabric lies in its use of IS-IS to create a naturally loop-free topology. This eliminates the inefficiencies of Spanning Tree Protocol, where redundant links remain idle. Instead, SPB leverages Equal Cost Multi-Pathing (ECMP) to ensure all physical links are active and carrying traffic. This approach maximizes hardware ROI by utilizing the full capacity of your infrastructure. Organizations often find that specialized training is the most effective way to help engineering teams master these advanced link-state behaviors.
The “Edge-Only” Provisioning Model
The “edge-only” model is perhaps the most transformative aspect of this architecture. In a legacy environment, adding a new service requires manual configuration at every “hop” from the access layer to the core. With Fabric Connect, services are provisioned only at the entry and exit points (the edge). The core remains service-agnostic, automatically learning and distributing service information without manual intervention. This dramatically reduces maintenance window requirements, as you no longer need to touch the core switches for routine service expansions. It’s a cleaner, more predictable method of scaling enterprise connectivity.
Operational Comparison: Provisioning, Scalability, and Security
Operational excellence is the hallmark of a modern enterprise network. When analyzing Extreme Networks Fabric Connect vs traditional VLANs, the difference in security posture and administrative efficiency is striking. Fabric Connect facilitates hyper-segmentation, allowing for thousands of isolated segments without the complexity of traditional Virtual Routing and Forwarding (VRF) instances. This capability enables IT teams to scale services rapidly while maintaining granular control over every traffic flow. Verified industry data suggests that this architecture can reduce manual configuration at the network edge by approximately 90%.
Hyper-segmentation vs. Traditional ACLs
Traditional VLAN-based security often relies on porous Access Control Lists (ACLs) that are notoriously difficult to maintain across a large campus. These legacy methods frequently suffer from configuration drift and human error. In contrast, Fabric Connect segments traffic at Layer 2 or Layer 3 with zero leakage between zones. This ensures that sensitive data remains isolated from guest users or compromised devices, providing a robust defense against lateral movement within the network.
Stealth Networking and Attack Surface Reduction
A unique differentiator of this architecture is “Stealth Networking.” Within the fabric, nodes do not require IP addresses for the control plane, making them invisible to external scanning tools. This effectively hides the network core from hackers, significantly reducing the available attack surface. It’s a strategic benefit for securing vulnerable IoT devices and guest networks that might otherwise serve as entry points for threats. We invite you to explore our Extreme Networks authorised training to master these security protocols.
By unifying the control plane, this technology simplifies troubleshooting. It reduces the mean time to repair (MTTR) significantly. Provisioning times drop from days to minutes, directly impacting your organization’s agility. This shift allows your staff to focus on strategic initiatives rather than manual maintenance tasks.
Strategic Implementation: Transitioning to Fabric Networking
Implementing a modern fabric requires a fundamental shift in organizational mindset. You move from the tedious task of managing individual boxes to the strategic orchestration of end-to-end services. This evolution ensures that the technical benefits of Extreme Networks Fabric Connect vs traditional VLANs are fully realized within your specific operational context. We recommend initiating this journey with a pilot phase, typically focused on a high-density data center environment or a specific campus wing, to establish a proven fabric seed before a wider rollout.
As an Extreme Networks Authorized Training Partner, we emphasize that professional enablement is the most critical factor for migration success. Preparing your team for the nuances of link-state protocols ensures that the transition is seamless and well-documented. This proactive approach minimizes the risks often associated with legacy network overhauls.
Bridging the Skills Gap
The move to fabric networking necessitates a transition from legacy STP and VLAN logic toward mastery of SPB and IS-IS behaviors. This evolution requires engineers to understand how the control plane handles service distribution without manual tagging. Enrolling in Extreme Networks Fabric Engine training provides the technical foundation needed to manage these automated environments. It’s a vital step for any team looking to eliminate the fragility of manual configuration errors.
Consultancy and Design Best Practices
Successful deployments often rely on precise architectural design and a clear migration roadmap. Professional consultancy helps in creating a robust initial fabric seed that can scale across global campuses without disruption. Insoft Services supports global enterprises by optimizing these complex infrastructures through expert guidance and localized expertise. We focus on enabling your IT staff to design resilient, future-ready architectures that leverage the full power of hyper-segmentation and stealth networking, ensuring your organization remains agile in an ever-changing professional landscape.
Future-Proofing Your Enterprise Infrastructure
Adopting an automated, service-centric architecture is no longer a luxury but a strategic necessity for global enterprises. By evaluating the benefits of Extreme Networks Fabric Connect vs traditional VLANs, it’s clear that the shift toward Shortest Path Bridging eliminates the inherent risks of manual configuration and unstable Spanning Tree environments. You’ve seen how hyper-segmentation and stealth networking significantly reduce your attack surface while increasing operational agility through edge-only provisioning. As an Authorized Extreme Networks Training Partner with global EMEA-wide delivery, we’re dedicated to providing the expert-led technical consultancy and skills your team needs for a successful migration.
We invite you to master modern network architectures with Official Extreme Networks Training at Insoft Services. It’s an investment in your organization’s long-term resilience and technical excellence. We look forward to supporting your professional growth as you build a more secure, efficient network for the future.
Frequently Asked Questions
Does Extreme Networks Fabric Connect require proprietary hardware?
Extreme Networks Fabric Connect requires hardware specifically designed to support the IEEE 802.1aq standard and the Fabric Engine operating system. While the underlying Shortest Path Bridging protocol is an open standard, the full benefits of the fabric architecture are realized through Extreme’s specialized hardware platforms. It’s important to verify that your switches support MAC-in-MAC encapsulation before beginning a deployment of Extreme Networks Fabric Connect vs traditional VLANs.
Can I run Fabric Connect alongside my existing traditional VLANs?
You can certainly operate Fabric Connect alongside your existing traditional VLANs during a phased migration. The architecture supports Transparent Port UNI and VLAN UNI modes, allowing the fabric to carry legacy 802.1Q tagged traffic without disruption. This capability enables organizations to maintain their current core-aggregation-access hierarchy while gradually introducing fabric services to specific campus wings or data center segments to ensure a stable and predictable transition.
How does Fabric Connect improve network recovery times compared to STP?
Fabric Connect significantly improves recovery times by replacing the slow convergence of Spanning Tree Protocol with the rapid link-state updates of IS-IS. In a traditional environment, STP might take up to 30 or 50 seconds to reroute traffic after a link failure. Fabric Connect typically achieves sub-second convergence, ensuring that critical applications and VoIP sessions remain stable even during physical link interruptions or unexpected hardware failures.
Is Fabric Connect more difficult to troubleshoot than traditional networking?
Troubleshooting is actually simplified because the fabric utilizes a single, unified control plane for all Layer 2 and Layer 3 services. In traditional networking, engineers must often correlate data across multiple protocols like OSPF, PIM, and STP. With Fabric Connect, you only manage IS-IS. This reduction in protocol complexity allows technical teams to identify and resolve connectivity issues much faster, lowering the overall mean time to repair.
What are the specific training requirements for a team to manage Fabric Connect?
Managing this architecture requires a shift from legacy 802.1Q logic to mastering Shortest Path Bridging and IS-IS link-state behaviors. We recommend that teams complete official Extreme Networks Fabric Engine training as a foundational step. This specific curriculum covers the configuration of I-SIDs, the implementation of hyper-segmentation, and the management of edge-only provisioning models to ensure your engineers are fully prepared for modern enterprise infrastructure demands.
What if your network core never required another manual configuration change, regardless of how many new services you deployed? For many IT leaders, the daily reality of managing enterprise infrastructure still involves the high-risk dance of hop-by-hop VLAN tagging and the constant threat of Spanning Tree Protocol loops. In the strategic comparison of Extreme Networks Fabric Connect vs traditional VLANs, it’s clear that legacy architectures struggle to keep pace with modern demands for agility and security. We understand that your technical team faces significant pressure to reduce service provisioning times across large campuses while maintaining absolute network stability.
This article will demonstrate how transitioning to a Shortest Path Bridging architecture simplifies your operations by automating the core and enabling hyper-segmentation. You’ll gain a comprehensive understanding of how Fabric Connect can reduce manual configuration at the network edge by approximately 90%, providing a clear justification for infrastructure modernization. We’ll examine the technical shift from legacy IEEE 802.1Q standards to the robust IEEE 802.1ah framework to help you achieve faster delivery for every new network service.
The Architecture of Complexity: Limitations of Traditional VLANs
Traditional network architectures rely on the IEEE 802.1Q standard, which necessitates a manual, hop-by-hop approach to configuration. Every switch in the communication path must be individually updated to support a new service. This method creates significant management overhead and introduces numerous opportunities for human error. When evaluating Extreme Networks Fabric Connect vs traditional VLANs, the contrast in operational efficiency becomes immediately apparent. In legacy environments, extending a single VLAN across multiple data centers often leads to “VLAN sprawl,” where the complexity of the database makes troubleshooting nearly impossible. Mastering these transitions often begins with Extreme Networks authorised training to understand the underlying shift in logic.
The Spanning Tree Protocol (STP) Burden
To prevent catastrophic network loops, traditional systems depend on STP. This protocol works by logically blocking redundant physical paths, which effectively wastes up to 50% of your available fiber bandwidth. When a link fails, the “convergence time” required for STP to recalculate and unblock a path can range from several seconds to nearly a minute, causing noticeable downtime for critical applications. This instability is a primary driver for moving toward the IEEE 802.1aq standard, which replaces these legacy limitations with more resilient multipath capabilities.
Manual Service Provisioning Hurdles
Provisioning a new service across a core-aggregation-access hierarchy is a fragile process. A single typo in a trunk configuration or a missing tag on an intermediate switch can isolate entire network segments. These manual tagging and trunking requirements don’t just slow down delivery; they create security vulnerabilities through misconfiguration. By comparing Extreme Networks Fabric Connect vs traditional VLANs, it’s clear that the manual burdens of the latter represent a significant strategic liability for growing enterprises. Relying on manual entries across dozens of switches invites inconsistencies that modern fabric architectures simply eliminate.
Extreme Networks Fabric Connect: A Simplified Approach
Extreme Networks Fabric Connect represents a paradigm shift in network design by utilizing a virtualized network architecture that eliminates the need for core-layer re-configuration. Unlike the fragmented protocol stacks of the past, this solution is built upon the IEEE 802.1aq Shortest Path Bridging (SPB) standard. By consolidating all routing and switching functions into a single, link-state protocol (IS-IS), it streamlines the control plane. This consolidation is technically grounded in IETF RFC 6329, which defines the IS-IS extensions necessary to support such a robust fabric. When comparing Extreme Networks Fabric Connect vs traditional VLANs, the primary advantage is the removal of multiple overlay protocols like OSPF, PIM, and STP.
Shortest Path Bridging (SPB) Explained
The intelligence of the fabric lies in its use of IS-IS to create a naturally loop-free topology. This eliminates the inefficiencies of Spanning Tree Protocol, where redundant links remain idle. Instead, SPB leverages Equal Cost Multi-Pathing (ECMP) to ensure all physical links are active and carrying traffic. This approach maximizes hardware ROI by utilizing the full capacity of your infrastructure. Organizations often find that specialized training is the most effective way to help engineering teams master these advanced link-state behaviors.
The “Edge-Only” Provisioning Model
The “edge-only” model is perhaps the most transformative aspect of this architecture. In a legacy environment, adding a new service requires manual configuration at every “hop” from the access layer to the core. With Fabric Connect, services are provisioned only at the entry and exit points (the edge). The core remains service-agnostic, automatically learning and distributing service information without manual intervention. This dramatically reduces maintenance window requirements, as you no longer need to touch the core switches for routine service expansions. It’s a cleaner, more predictable method of scaling enterprise connectivity.
Operational Comparison: Provisioning, Scalability, and Security
Operational excellence is the hallmark of a modern enterprise network. When analyzing Extreme Networks Fabric Connect vs traditional VLANs, the difference in security posture and administrative efficiency is striking. Fabric Connect facilitates hyper-segmentation, allowing for thousands of isolated segments without the complexity of traditional Virtual Routing and Forwarding (VRF) instances. This capability enables IT teams to scale services rapidly while maintaining granular control over every traffic flow. Verified industry data suggests that this architecture can reduce manual configuration at the network edge by approximately 90%.
Hyper-segmentation vs. Traditional ACLs
Traditional VLAN-based security often relies on porous Access Control Lists (ACLs) that are notoriously difficult to maintain across a large campus. These legacy methods frequently suffer from configuration drift and human error. In contrast, Fabric Connect segments traffic at Layer 2 or Layer 3 with zero leakage between zones. This ensures that sensitive data remains isolated from guest users or compromised devices, providing a robust defense against lateral movement within the network.
Stealth Networking and Attack Surface Reduction
A unique differentiator of this architecture is “Stealth Networking.” Within the fabric, nodes do not require IP addresses for the control plane, making them invisible to external scanning tools. This effectively hides the network core from hackers, significantly reducing the available attack surface. It’s a strategic benefit for securing vulnerable IoT devices and guest networks that might otherwise serve as entry points for threats. We invite you to explore our Extreme Networks authorised training to master these security protocols.
By unifying the control plane, this technology simplifies troubleshooting. It reduces the mean time to repair (MTTR) significantly. Provisioning times drop from days to minutes, directly impacting your organization’s agility. This shift allows your staff to focus on strategic initiatives rather than manual maintenance tasks.
Strategic Implementation: Transitioning to Fabric Networking
Implementing a modern fabric requires a fundamental shift in organizational mindset. You move from the tedious task of managing individual boxes to the strategic orchestration of end-to-end services. This evolution ensures that the technical benefits of Extreme Networks Fabric Connect vs traditional VLANs are fully realized within your specific operational context. We recommend initiating this journey with a pilot phase, typically focused on a high-density data center environment or a specific campus wing, to establish a proven fabric seed before a wider rollout.
As an Extreme Networks Authorized Training Partner, we emphasize that professional enablement is the most critical factor for migration success. Preparing your team for the nuances of link-state protocols ensures that the transition is seamless and well-documented. This proactive approach minimizes the risks often associated with legacy network overhauls.
Bridging the Skills Gap
The move to fabric networking necessitates a transition from legacy STP and VLAN logic toward mastery of SPB and IS-IS behaviors. This evolution requires engineers to understand how the control plane handles service distribution without manual tagging. Enrolling in Extreme Networks Fabric Engine training provides the technical foundation needed to manage these automated environments. It’s a vital step for any team looking to eliminate the fragility of manual configuration errors.
Consultancy and Design Best Practices
Successful deployments often rely on precise architectural design and a clear migration roadmap. Professional consultancy helps in creating a robust initial fabric seed that can scale across global campuses without disruption. Insoft Services supports global enterprises by optimizing these complex infrastructures through expert guidance and localized expertise. We focus on enabling your IT staff to design resilient, future-ready architectures that leverage the full power of hyper-segmentation and stealth networking, ensuring your organization remains agile in an ever-changing professional landscape.
Future-Proofing Your Enterprise Infrastructure
Adopting an automated, service-centric architecture is no longer a luxury but a strategic necessity for global enterprises. By evaluating the benefits of Extreme Networks Fabric Connect vs traditional VLANs, it’s clear that the shift toward Shortest Path Bridging eliminates the inherent risks of manual configuration and unstable Spanning Tree environments. You’ve seen how hyper-segmentation and stealth networking significantly reduce your attack surface while increasing operational agility through edge-only provisioning. As an Authorized Extreme Networks Training Partner with global EMEA-wide delivery, we’re dedicated to providing the expert-led technical consultancy and skills your team needs for a successful migration.
We invite you to master modern network architectures with Official Extreme Networks Training at Insoft Services. It’s an investment in your organization’s long-term resilience and technical excellence. We look forward to supporting your professional growth as you build a more secure, efficient network for the future.
Frequently Asked Questions
Does Extreme Networks Fabric Connect require proprietary hardware?
Extreme Networks Fabric Connect requires hardware specifically designed to support the IEEE 802.1aq standard and the Fabric Engine operating system. While the underlying Shortest Path Bridging protocol is an open standard, the full benefits of the fabric architecture are realized through Extreme’s specialized hardware platforms. It’s important to verify that your switches support MAC-in-MAC encapsulation before beginning a deployment of Extreme Networks Fabric Connect vs traditional VLANs.
Can I run Fabric Connect alongside my existing traditional VLANs?
You can certainly operate Fabric Connect alongside your existing traditional VLANs during a phased migration. The architecture supports Transparent Port UNI and VLAN UNI modes, allowing the fabric to carry legacy 802.1Q tagged traffic without disruption. This capability enables organizations to maintain their current core-aggregation-access hierarchy while gradually introducing fabric services to specific campus wings or data center segments to ensure a stable and predictable transition.
How does Fabric Connect improve network recovery times compared to STP?
Fabric Connect significantly improves recovery times by replacing the slow convergence of Spanning Tree Protocol with the rapid link-state updates of IS-IS. In a traditional environment, STP might take up to 30 or 50 seconds to reroute traffic after a link failure. Fabric Connect typically achieves sub-second convergence, ensuring that critical applications and VoIP sessions remain stable even during physical link interruptions or unexpected hardware failures.
Is Fabric Connect more difficult to troubleshoot than traditional networking?
Troubleshooting is actually simplified because the fabric utilizes a single, unified control plane for all Layer 2 and Layer 3 services. In traditional networking, engineers must often correlate data across multiple protocols like OSPF, PIM, and STP. With Fabric Connect, you only manage IS-IS. This reduction in protocol complexity allows technical teams to identify and resolve connectivity issues much faster, lowering the overall mean time to repair.
What are the specific training requirements for a team to manage Fabric Connect?
Managing this architecture requires a shift from legacy 802.1Q logic to mastering Shortest Path Bridging and IS-IS link-state behaviors. We recommend that teams complete official Extreme Networks Fabric Engine training as a foundational step. This specific curriculum covers the configuration of I-SIDs, the implementation of hyper-segmentation, and the management of edge-only provisioning models to ensure your engineers are fully prepared for modern enterprise infrastructure demands.
What if your network core never required another manual configuration change, regardless of how many new services you deployed? For many IT leaders, the daily reality of managing enterprise infrastructure still involves the high-risk dance of hop-by-hop VLAN tagging and the constant threat of Spanning Tree Protocol loops. In the strategic comparison of Extreme Networks Fabric Connect vs traditional VLANs, it’s clear that legacy architectures struggle to keep pace with modern demands for agility and security. We understand that your technical team faces significant pressure to reduce service provisioning times across large campuses while maintaining absolute network stability.
This article will demonstrate how transitioning to a Shortest Path Bridging architecture simplifies your operations by automating the core and enabling hyper-segmentation. You’ll gain a comprehensive understanding of how Fabric Connect can reduce manual configuration at the network edge by approximately 90%, providing a clear justification for infrastructure modernization. We’ll examine the technical shift from legacy IEEE 802.1Q standards to the robust IEEE 802.1ah framework to help you achieve faster delivery for every new network service.
The Architecture of Complexity: Limitations of Traditional VLANs
Traditional network architectures rely on the IEEE 802.1Q standard, which necessitates a manual, hop-by-hop approach to configuration. Every switch in the communication path must be individually updated to support a new service. This method creates significant management overhead and introduces numerous opportunities for human error. When evaluating Extreme Networks Fabric Connect vs traditional VLANs, the contrast in operational efficiency becomes immediately apparent. In legacy environments, extending a single VLAN across multiple data centers often leads to “VLAN sprawl,” where the complexity of the database makes troubleshooting nearly impossible. Mastering these transitions often begins with Extreme Networks authorised training to understand the underlying shift in logic.
The Spanning Tree Protocol (STP) Burden
To prevent catastrophic network loops, traditional systems depend on STP. This protocol works by logically blocking redundant physical paths, which effectively wastes up to 50% of your available fiber bandwidth. When a link fails, the “convergence time” required for STP to recalculate and unblock a path can range from several seconds to nearly a minute, causing noticeable downtime for critical applications. This instability is a primary driver for moving toward the IEEE 802.1aq standard, which replaces these legacy limitations with more resilient multipath capabilities.
Manual Service Provisioning Hurdles
Provisioning a new service across a core-aggregation-access hierarchy is a fragile process. A single typo in a trunk configuration or a missing tag on an intermediate switch can isolate entire network segments. These manual tagging and trunking requirements don’t just slow down delivery; they create security vulnerabilities through misconfiguration. By comparing Extreme Networks Fabric Connect vs traditional VLANs, it’s clear that the manual burdens of the latter represent a significant strategic liability for growing enterprises. Relying on manual entries across dozens of switches invites inconsistencies that modern fabric architectures simply eliminate.
Extreme Networks Fabric Connect: A Simplified Approach
Extreme Networks Fabric Connect represents a paradigm shift in network design by utilizing a virtualized network architecture that eliminates the need for core-layer re-configuration. Unlike the fragmented protocol stacks of the past, this solution is built upon the IEEE 802.1aq Shortest Path Bridging (SPB) standard. By consolidating all routing and switching functions into a single, link-state protocol (IS-IS), it streamlines the control plane. This consolidation is technically grounded in IETF RFC 6329, which defines the IS-IS extensions necessary to support such a robust fabric. When comparing Extreme Networks Fabric Connect vs traditional VLANs, the primary advantage is the removal of multiple overlay protocols like OSPF, PIM, and STP.
Shortest Path Bridging (SPB) Explained
The intelligence of the fabric lies in its use of IS-IS to create a naturally loop-free topology. This eliminates the inefficiencies of Spanning Tree Protocol, where redundant links remain idle. Instead, SPB leverages Equal Cost Multi-Pathing (ECMP) to ensure all physical links are active and carrying traffic. This approach maximizes hardware ROI by utilizing the full capacity of your infrastructure. Organizations often find that specialized training is the most effective way to help engineering teams master these advanced link-state behaviors.
The “Edge-Only” Provisioning Model
The “edge-only” model is perhaps the most transformative aspect of this architecture. In a legacy environment, adding a new service requires manual configuration at every “hop” from the access layer to the core. With Fabric Connect, services are provisioned only at the entry and exit points (the edge). The core remains service-agnostic, automatically learning and distributing service information without manual intervention. This dramatically reduces maintenance window requirements, as you no longer need to touch the core switches for routine service expansions. It’s a cleaner, more predictable method of scaling enterprise connectivity.
Operational Comparison: Provisioning, Scalability, and Security
Operational excellence is the hallmark of a modern enterprise network. When analyzing Extreme Networks Fabric Connect vs traditional VLANs, the difference in security posture and administrative efficiency is striking. Fabric Connect facilitates hyper-segmentation, allowing for thousands of isolated segments without the complexity of traditional Virtual Routing and Forwarding (VRF) instances. This capability enables IT teams to scale services rapidly while maintaining granular control over every traffic flow. Verified industry data suggests that this architecture can reduce manual configuration at the network edge by approximately 90%.
Hyper-segmentation vs. Traditional ACLs
Traditional VLAN-based security often relies on porous Access Control Lists (ACLs) that are notoriously difficult to maintain across a large campus. These legacy methods frequently suffer from configuration drift and human error. In contrast, Fabric Connect segments traffic at Layer 2 or Layer 3 with zero leakage between zones. This ensures that sensitive data remains isolated from guest users or compromised devices, providing a robust defense against lateral movement within the network.
Stealth Networking and Attack Surface Reduction
A unique differentiator of this architecture is “Stealth Networking.” Within the fabric, nodes do not require IP addresses for the control plane, making them invisible to external scanning tools. This effectively hides the network core from hackers, significantly reducing the available attack surface. It’s a strategic benefit for securing vulnerable IoT devices and guest networks that might otherwise serve as entry points for threats. We invite you to explore our Extreme Networks authorised training to master these security protocols.
By unifying the control plane, this technology simplifies troubleshooting. It reduces the mean time to repair (MTTR) significantly. Provisioning times drop from days to minutes, directly impacting your organization’s agility. This shift allows your staff to focus on strategic initiatives rather than manual maintenance tasks.
Strategic Implementation: Transitioning to Fabric Networking
Implementing a modern fabric requires a fundamental shift in organizational mindset. You move from the tedious task of managing individual boxes to the strategic orchestration of end-to-end services. This evolution ensures that the technical benefits of Extreme Networks Fabric Connect vs traditional VLANs are fully realized within your specific operational context. We recommend initiating this journey with a pilot phase, typically focused on a high-density data center environment or a specific campus wing, to establish a proven fabric seed before a wider rollout.
As an Extreme Networks Authorized Training Partner, we emphasize that professional enablement is the most critical factor for migration success. Preparing your team for the nuances of link-state protocols ensures that the transition is seamless and well-documented. This proactive approach minimizes the risks often associated with legacy network overhauls.
Bridging the Skills Gap
The move to fabric networking necessitates a transition from legacy STP and VLAN logic toward mastery of SPB and IS-IS behaviors. This evolution requires engineers to understand how the control plane handles service distribution without manual tagging. Enrolling in Extreme Networks Fabric Engine training provides the technical foundation needed to manage these automated environments. It’s a vital step for any team looking to eliminate the fragility of manual configuration errors.
Consultancy and Design Best Practices
Successful deployments often rely on precise architectural design and a clear migration roadmap. Professional consultancy helps in creating a robust initial fabric seed that can scale across global campuses without disruption. Insoft Services supports global enterprises by optimizing these complex infrastructures through expert guidance and localized expertise. We focus on enabling your IT staff to design resilient, future-ready architectures that leverage the full power of hyper-segmentation and stealth networking, ensuring your organization remains agile in an ever-changing professional landscape.
Future-Proofing Your Enterprise Infrastructure
Adopting an automated, service-centric architecture is no longer a luxury but a strategic necessity for global enterprises. By evaluating the benefits of Extreme Networks Fabric Connect vs traditional VLANs, it’s clear that the shift toward Shortest Path Bridging eliminates the inherent risks of manual configuration and unstable Spanning Tree environments. You’ve seen how hyper-segmentation and stealth networking significantly reduce your attack surface while increasing operational agility through edge-only provisioning. As an Authorized Extreme Networks Training Partner with global EMEA-wide delivery, we’re dedicated to providing the expert-led technical consultancy and skills your team needs for a successful migration.
We invite you to master modern network architectures with Official Extreme Networks Training at Insoft Services. It’s an investment in your organization’s long-term resilience and technical excellence. We look forward to supporting your professional growth as you build a more secure, efficient network for the future.
Frequently Asked Questions
Does Extreme Networks Fabric Connect require proprietary hardware?
Extreme Networks Fabric Connect requires hardware specifically designed to support the IEEE 802.1aq standard and the Fabric Engine operating system. While the underlying Shortest Path Bridging protocol is an open standard, the full benefits of the fabric architecture are realized through Extreme’s specialized hardware platforms. It’s important to verify that your switches support MAC-in-MAC encapsulation before beginning a deployment of Extreme Networks Fabric Connect vs traditional VLANs.
Can I run Fabric Connect alongside my existing traditional VLANs?
You can certainly operate Fabric Connect alongside your existing traditional VLANs during a phased migration. The architecture supports Transparent Port UNI and VLAN UNI modes, allowing the fabric to carry legacy 802.1Q tagged traffic without disruption. This capability enables organizations to maintain their current core-aggregation-access hierarchy while gradually introducing fabric services to specific campus wings or data center segments to ensure a stable and predictable transition.
How does Fabric Connect improve network recovery times compared to STP?
Fabric Connect significantly improves recovery times by replacing the slow convergence of Spanning Tree Protocol with the rapid link-state updates of IS-IS. In a traditional environment, STP might take up to 30 or 50 seconds to reroute traffic after a link failure. Fabric Connect typically achieves sub-second convergence, ensuring that critical applications and VoIP sessions remain stable even during physical link interruptions or unexpected hardware failures.
Is Fabric Connect more difficult to troubleshoot than traditional networking?
Troubleshooting is actually simplified because the fabric utilizes a single, unified control plane for all Layer 2 and Layer 3 services. In traditional networking, engineers must often correlate data across multiple protocols like OSPF, PIM, and STP. With Fabric Connect, you only manage IS-IS. This reduction in protocol complexity allows technical teams to identify and resolve connectivity issues much faster, lowering the overall mean time to repair.
What are the specific training requirements for a team to manage Fabric Connect?
Managing this architecture requires a shift from legacy 802.1Q logic to mastering Shortest Path Bridging and IS-IS link-state behaviors. We recommend that teams complete official Extreme Networks Fabric Engine training as a foundational step. This specific curriculum covers the configuration of I-SIDs, the implementation of hyper-segmentation, and the management of edge-only provisioning models to ensure your engineers are fully prepared for modern enterprise infrastructure demands.
No Comments