 Finland
 Germany
 Denmark
 Sweden
 Italy
 Netherlands
 Norway

With 60% of organizations citing skills gaps as their primary workforce hurdle and 4.8 million roles remaining unfilled globally, losing seasoned engineers to marginal salary bumps isn’t merely frustrating; it presents a substantial operational risk. You likely know how exhausting it is to watch training investments evaporate into fragmented, unaccredited courses while perimeter blind spots persist across complex multi-vendor networks. Developing a structured cybersecurity professional development plan provides the definitive remedy, transforming disjointed upskilling into measurable competence and genuine organizational loyalty.
We invite you to discover how to design an enterprise-grade cybersecurity professional development plan that accelerates technical competencies and strengthens staff retention across your security operations. In this guide, we detail a repeatable 12-month development blueprint across all engineering tiers. You’ll gain practical, proven strategies to shorten incident response intervals, maintain rigorous regulatory audit compliance, and substantially curtail costly recruitment expenditures through structured internal career progression.
The Strategic Architecture of a Cybersecurity Professional Development Plan
An enterprise-grade cybersecurity professional development plan serves as an operational capability framework rather than a casual training checklist. By embedding continuous education into daily governance, security leaders transform skill acquisition into a proactive defensive control. Documented career paths directly mitigate security operations center (SOC) burnout, giving analysts clear milestones beyond relentless ticket queues while reducing vulnerability windows across critical infrastructure.
Bridging Organizational Security Objectives with Individual Aspirations
Effective workforce enablement aligns defensive roadmap gaps with individual technical ambitions. Frameworks like the National Initiative for Cybersecurity Education (NICE) establish standardized competencies, yet enterprise success requires tailored execution. Courteous, quarterly talent dialogues help leaders identify whether an engineer prefers cloud perimeter defense or threat hunting. Connecting these preferences directly to upcoming audit milestones, such as ISO/IEC 27001:2022 surveillance reviews or DORA compliance requirements, ensures personal advancement directly bolsters perimeter resilience.
The Business Economics of Retention Versus External Recruitment
Replacing specialized cyber talent drains both capital and institutional memory. Consider the operational realities:
- Filling senior security engineering roles routinely requires six months or longer across the industry.
- Aggressive headhunters frequently lure analysts away with marginal compensation bumps when internal progression stalls.
- Structured enablement through an authorized enterprise course catalog costs substantially less than third-party recruitment placement fees.
Transparent promotional pathways deter talent poaching by demonstrating tangible internal growth. When engineers see funded learning pathways, their commitment to the organization deepens, protecting both security postures and recruitment budgets.
Core Phases of an Enterprise Cybersecurity Skills Progression Pathway
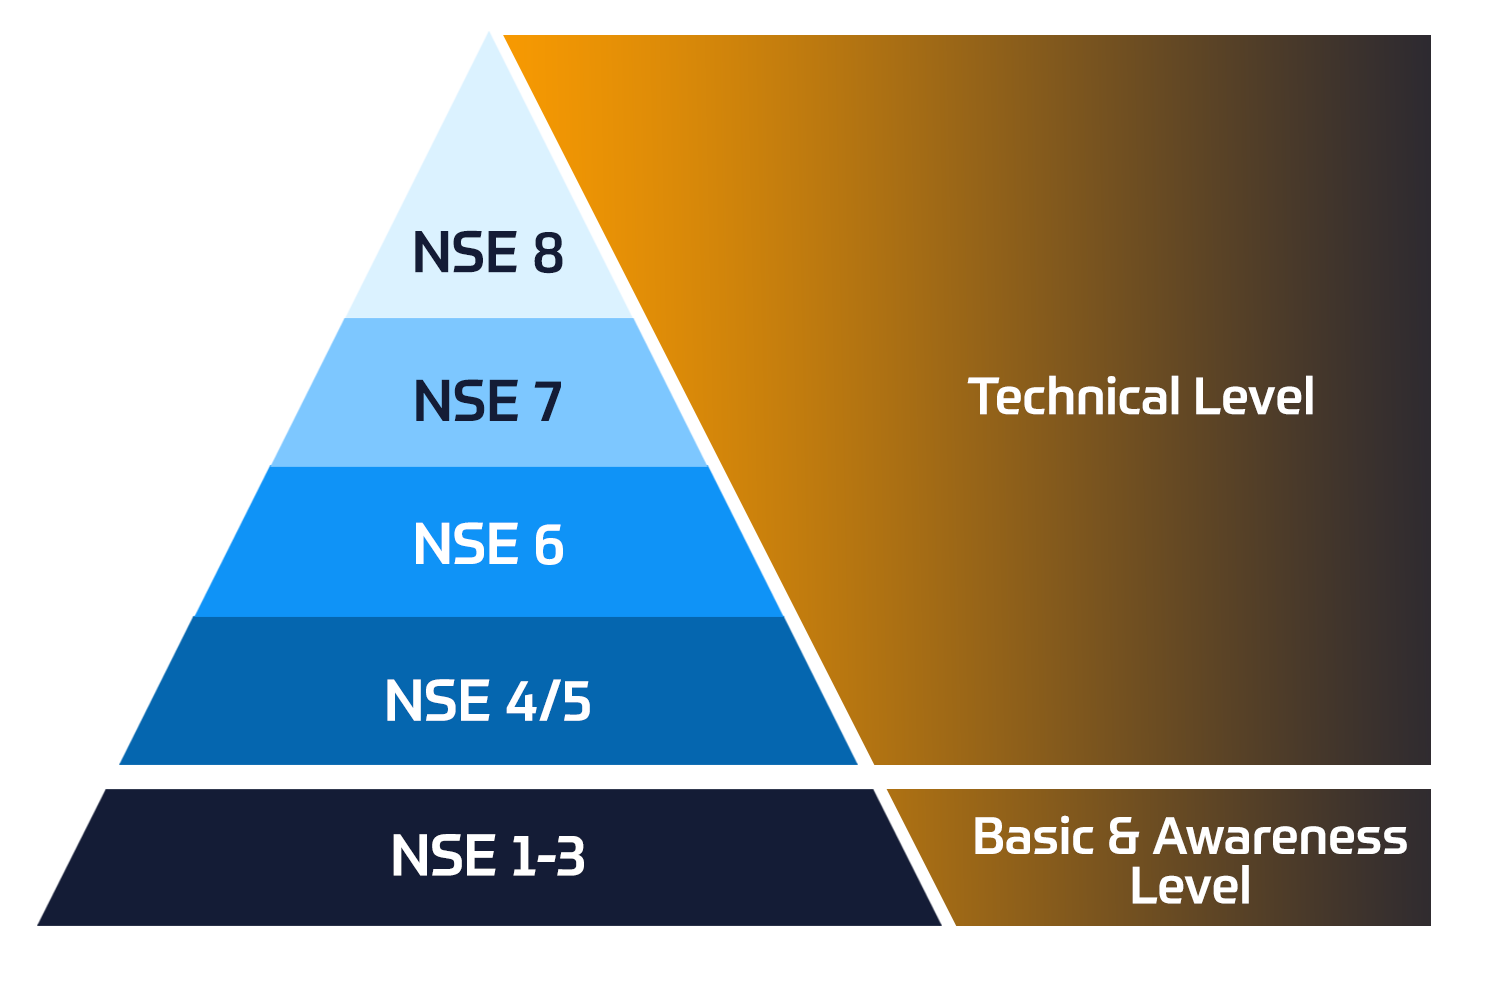
A scalable cybersecurity professional development plan divides capability growth into four sequential stages: foundational infrastructure, defensive system administration, advanced engineering, and strategic architecture. Objective skill validation requires recognized vendor testing rather than informal peer reviews, ensuring engineers demonstrate measurable proficiency in live production environments.
Foundational Competencies and Infrastructure Security Mastery
Security personnel cannot defend traffic patterns they don’t fully understand. Tier-1 engineers require an exhaustive grasp of subnetting, Layer 2 switching, BGP and OSPF routing protocols, and stateful packet inspection. Aligning early staff onboarding with CISA’s workforce development initiatives establishes strong baseline rigor. Completing formal programs such as the CCNA training track ensures your defenders diagnose anomalous traffic and isolate misconfigured access control lists quickly and accurately.
Advanced Defensive Engineering and Architecture Specializations
After mastering networking baselines, personnel transition into perimeter fortification and threat prevention. Advanced engineers evaluate Next-Generation Firewall policies, configure automated telemetry feeds, and enforce zero-trust segmentation across distributed enterprise sites.
Cultivating multi-vendor expertise transforms capable administrators into versatile security architects. Reviewing an authorized Fortinet certifications track provides senior analysts with a clear route from core firewall operations to unified threat fabric architectures. This transparent progression elevates technical competence across your entire team while giving experienced engineers an engaging, structured future within your organization.
Overcoming Operational Constraints: Integrating Learning into Active Workflows
Security leaders understandably worry that scheduling intensive coursework degrades live incident triage coverage. A mature cybersecurity professional development plan resolves this tension by formalizing protected, rostered developmental blocks within shift schedules. Pairing virtual instructor-led coursework with hands-on sandbox labs lets engineers hone defensive reflexes safely, preventing production disruptions while maintaining operational vigilance across every shift.
Implementing Modular and Asynchronous Learning Modalities
Expecting analysts to sacrifice personal evenings breeds burnout and employee resentment. Instead, structured operations utilize rotational peer coverage to protect dedicated study windows during working hours. Leveraging Cisco digital learning enables engineers to digest modular technical courses between active monitoring cycles. This steady cadence preserves study momentum while analysts immediately apply packet analysis techniques to live operational handovers.
Maximizing Enterprise Training Budgets and Enterprise Learning Credits
Valuable training allocations frequently sit dormant on vendor accounts until they quietly expire at year-end. Organizations can avoid wasted capital by establishing a routine review of enterprise software and licensing agreements. Maximize your technical enablement funds by redeeming verified Cisco learning credits for authorized instruction, ensuring your workforce development initiatives remain comprehensively supported without demanding supplemental capital outlays.
Operationalizing the Roadmap: Sustaining Long-Term Team Engagement
Sustaining momentum across an enterprise cybersecurity professional development plan requires consistent managerial follow-through. Conducting quarterly developmental reviews ensures engineers receive polite, constructive feedback while charting their next architectural milestones. Linking accredited certifications directly to transparent, merit-based compensation adjustments creates authentic incentives. Rotational assignments between SOC monitoring, network engineering, and governance teams expand technical perspective, keeping staff engaged while building multifaceted defensive capabilities.
Mentorship, Practical Sandboxes, and Internal Knowledge Transfer
Classroom learning yields lasting results when reinforced by day-to-day collaboration. Pairing junior analysts with senior engineers during live incident escalations accelerates operational troubleshooting. Certified engineers can lead monthly “lunch-and-learn” briefings, dissecting new threat behaviors or configuration practices for peers. Running quarterly purple-team sandboxes gives defenders a safe environment to test active mitigation tactics against simulated intrusions, directly validating applied technical skill.
Selecting an Authorized Global Training Partner
Generic bootcamps often fail to address enterprise-grade complexity. Selecting an authorized partner ensures staff learn directly from vendor-certified instructors who operate in active production ecosystems:
- Partnering with an authorized Cisco Learning Partner delivers certified instruction covering core routing, enterprise switching, and automated infrastructure defense.
- Leveraging a recognized Fortinet Premier Authorized Training Center ensures teams gain hands-on proficiency with carrier-class firewalls and integrated threat fabrics.
- Engaging an accredited provider for Extreme Networks training builds deep competency in fabric networking and zero-trust edge protection.
Formalizing enterprise learning agreements provides multi-vendor breadth across cloud, networking, and security disciplines. This comprehensive approach turns your cybersecurity professional development plan into a sustainable engine for operational excellence and long-term engineer retention.
Transforming Talent Strategy into Long-Term Defensive Resilience
Implementing an enterprise-grade cybersecurity professional development plan empowers your organization to outpace evolving threats while safeguarding invaluable institutional knowledge. By transforming disjointed upskilling into structured technical progression, you eliminate critical perimeter blind spots and insulate your operations from disruptive talent turnover. Scheduling protected developmental hours during regular operational shifts demonstrates genuine respect for your personnel, converting retention challenges into lasting organizational strength.
As an official Cisco Learning Partner and Fortinet Premier Authorized Training Center, Insoft Services delivers vendor-accredited education globally across virtual instructor-led, classroom, and flexible on-demand modalities. We warmly invite you to explore authorized enterprise cybersecurity training pathways with Insoft Services to equip your engineering tiers with the verified competencies required to defend complex networks. Cultivating your engineers systematically ensures your operational resilience remains uncompromised.
Frequently Asked Questions
How much working time should an enterprise allocate toward cybersecurity professional development?
Enterprises typically allocate four to eight hours per week, representing roughly ten percent of an engineer’s operational time. Incorporating these dedicated hours into a structured cybersecurity professional development plan ensures defensive personnel sharpen their technical skills without degrading shift coverage. Treating this developmental investment as a core operational duty protects analysts from burnout and keeps internal systems aligned with modern compliance standards.
Can an authorized professional development plan prevent skilled engineers from leaving our organization?
Yes, formal roadmaps significantly reduce voluntary turnover by establishing transparent advancement opportunities. When engineers see explicit milestones linked to accredited certifications and compensation reviews, they don’t jump for marginal salary bumps from competitors. A comprehensive cybersecurity professional development plan institutionalizes internal career mobility, proving to your technical staff that long-term professional growth thrives directly within your organization.
What is the practical difference between general cybersecurity credentials and vendor-authorized certifications?
General security credentials primarily emphasize theoretical frameworks, regulatory definitions, and administrative concepts. Conversely, vendor-authorized certifications from providers like Cisco or Fortinet demand practical, hands-on configuration mastery in rigorous laboratory environments. Certified personnel can immediately apply packet inspection rules, optimize firewall fabrics, and isolate network anomalies in complex enterprise production infrastructures without requiring protracted post-hire onboarding.
How do small security teams manage on-call responsibilities while attending intensive technical courses?
Small security teams successfully balance operational readiness by implementing modular, on-demand digital learning tracks alongside rotational coverage schedules. Instead of removing entire tiers for week-long sessions, departments schedule staggered virtual instructor-led training. Designating secondary on-call responders during active instruction hours shields attending analysts from routine alerts, allowing them to focus entirely on advanced technical exercises.
How should organizations handle team members who fail rigorous technical certification examinations?
Organizations should handle exam setbacks with courtesy and constructive support rather than punitive measures. High-level technical certifications are intentionally demanding. Managers should review the examination score report to identify specific domain deficiencies, allocate supplemental sandbox lab hours, and schedule a retake within thirty to sixty days. This supportive approach builds resilience, reinforces trust, and encourages continued engineering excellence.
No Comments